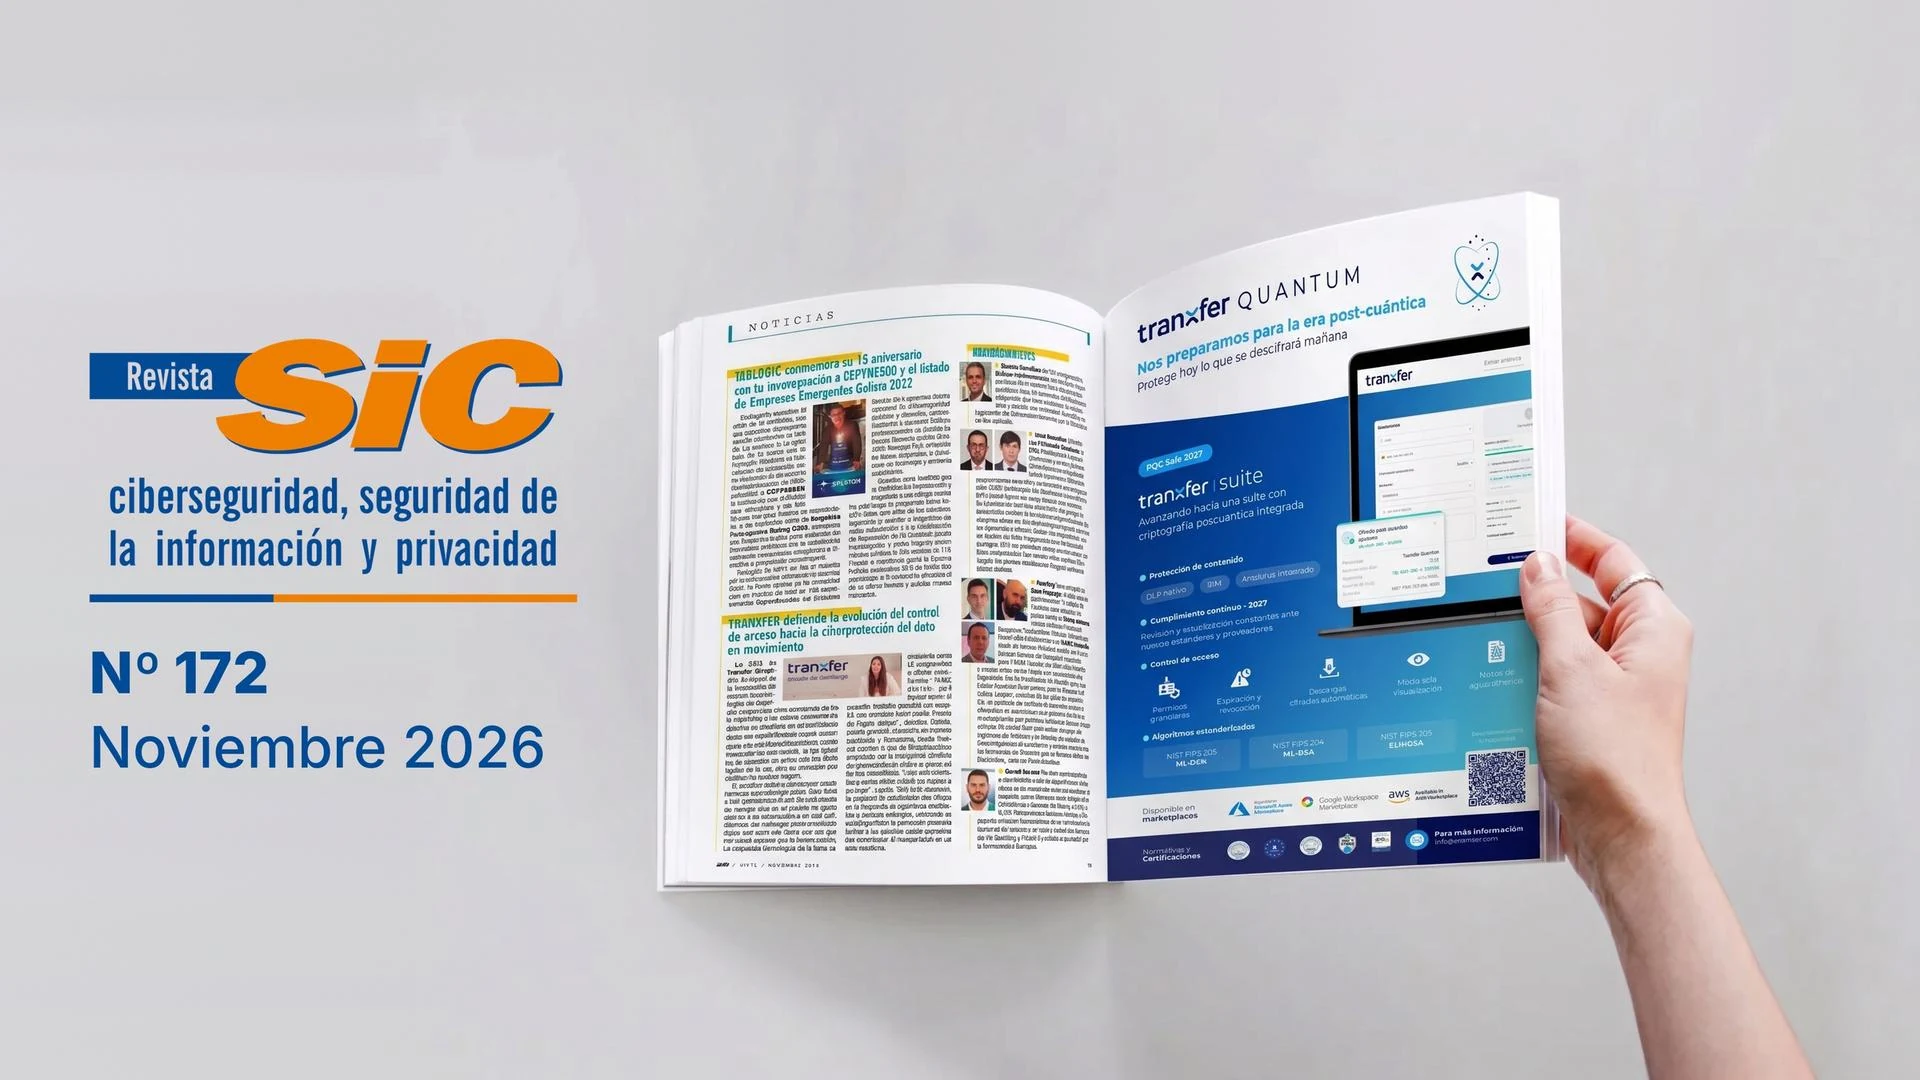
The November issue of Revista SIC (nº172), one of Spain’s leading cybersecurity publications, features Tranxfer’s view on one of today’s key challenges in corporate security: protecting information once it leaves the organization. The same issue also presents Tranxfer Quantum, our roadmap for the post-quantum era.
The challenge is no longer keeping data in, but letting it move securely
In the article, our CEO Eli Bernal explains why security strategies need to adapt to an environment where regulation and new threats are redefining the corporate perimeter.
Organizations work hand in hand with clients, suppliers and partners, and share information with them every day. In this context, the goal is no longer to stop data from leaving the network, but to make sure it moves securely.
Zero Trust and SASE: real progress, but with a gap
Architectures such as Zero Trust and SASE platforms have brought real progress in controlling who can access information and under what conditions. However, they leave a gap once data leaves the organization.
That is where Tranxfer fits in, as a complement to those platforms:
“SASE decides what the user can do. Tranxfer makes sure that what they need to do can be done securely.”
This is especially relevant in regulated and financial sectors. There, advanced infrastructure sits alongside the daily exchange of critical documents by email, something regulations such as DORA and NIS2 now require organizations to fix.
Tranxfer Quantum: getting ready for the post-quantum era
The threat known as harvest now, decrypt later means intercepting encrypted data today in order to decrypt it once quantum computing makes it possible. Information exchanged today therefore needs protection designed for tomorrow.
Tranxfer Quantum is a structured process with specific dates, reviewed every quarter:
Diagnosis and governance (in progress, July–December 2026): a complete cryptographic inventory (CBOM) and the creation of a Cryptographic Review Committee.
PQC migration (Q2 2027): adoption of the NIST-standardized algorithms (FIPS 203 ML-KEM, FIPS 204 ML-DSA and FIPS 205 SLH-DSA) across the entire platform, starting with critical and exposed systems.
Continuous compliance (from 2027): ongoing review against new standards, NIST guidance and vendors.
This approach is built on prevention: anticipating risk costs far less than recovering from a cyber incident.
Read it in Revista SIC
You can read the article and the Tranxfer Quantum page in the digital edition of Revista SIC nº172 (November 2026), on pages 69 and 32 respectively. The magazine is in Spanish.
👉 Read Revista SIC nº172
👉 Discover the Tranxfer Quantum roadmap